 Help Center
Set Up Your Account
Set Up Your Account
Roles & Permissions (Role-Based Access Control)
| Where to find it | Settings → User & teams → Roles & permissions Open Roles & Permissions |
|---|---|
| Who can do this | Users whose role includes role management, usually the Owner or an Admin. |
| Before you start | Know which jobs your team members actually do. Roles are easier to design around responsibilities than around individuals. |
| Time needed | About 5 minutes to review the built-in roles. About 10 minutes to build a custom one. |
A role is a set of permissions. Every user has exactly one role, and that role decides which pages they can open, which records they can see, and which actions they can take.
Roles are defined here, but assigned on the Users page. To change who has which role, go to Settings → User & teams → Users. See Managing Users.
The Roles Page
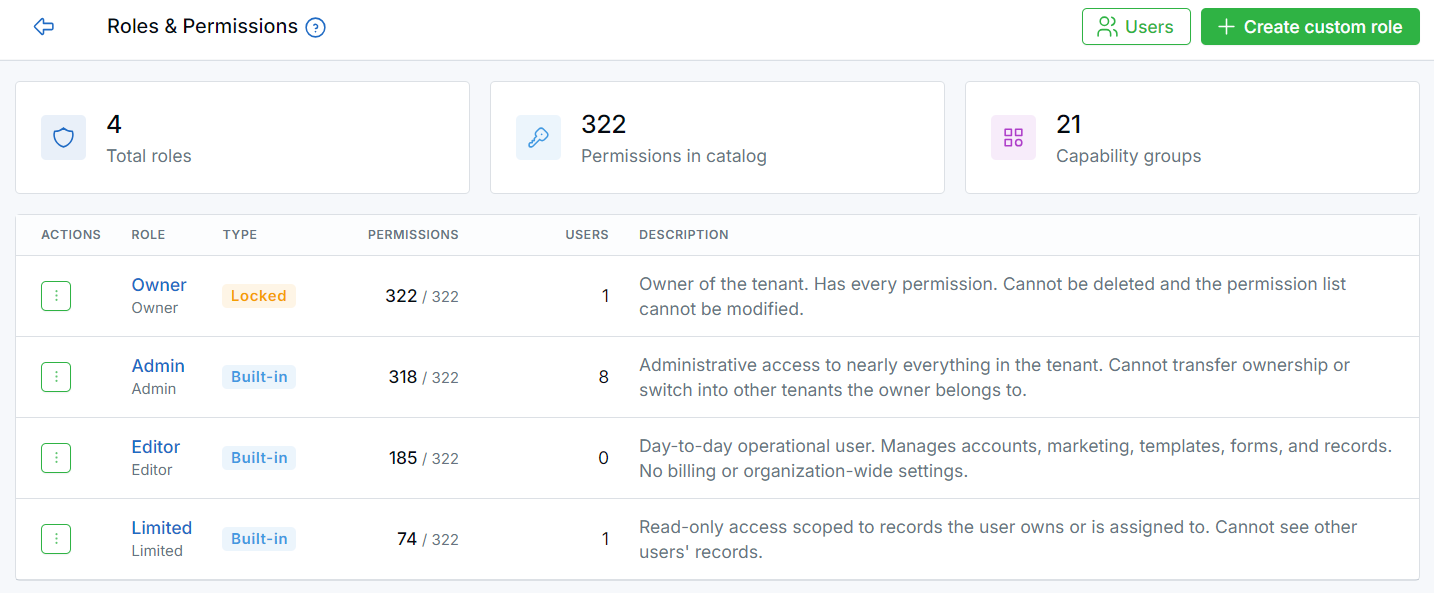
The Roles & Permissions page.
Three summary figures sit at the top:
- Total roles: built-in plus custom roles in your account.
- Permissions in catalog: every permission available to assign.
- Capability groups: the groups those permissions are organized into.
The table below shows each role, how many permissions it has, and how many users hold it.
| Badge | Meaning |
|---|---|
| Locked | Built-in. Cannot be edited or deleted, and always holds every permission. Only the Owner role. |
| Built-in | Ships with LeadCenter. Permissions can be edited, but the role cannot be deleted. |
| Custom | Created by your team. Fully editable and deletable. |
The Built-In Roles
| Role | Intended for |
|---|---|
| Owner Locked |
The account owner. Holds every permission. There is exactly one Owner per account, and the role cannot be edited or deleted. |
| Admin | Administrative access to nearly everything. Cannot transfer ownership. |
| Editor | Day-to-day operational work: accounts, marketing, templates, forms, and records. No billing or organization-wide settings. |
| Limited | Sees only the contacts and records the user owns or is assigned to, and can still add and edit those records, including uploading and deleting documents. |
Editing a built-in role only affects your account. Adjusting Admin, Editor, or Limited creates your own copy. Nothing changes for anyone else.
Capability Groups
Permissions are organized into capability groups, shown as expandable sections in the permission picker. Rather than reading every individual permission, decide at the group level first, then fine-tune inside the groups that matter.
Your total may differ from this list. Every account sees the same groups, except Reports, which appears only when your account has report categories.
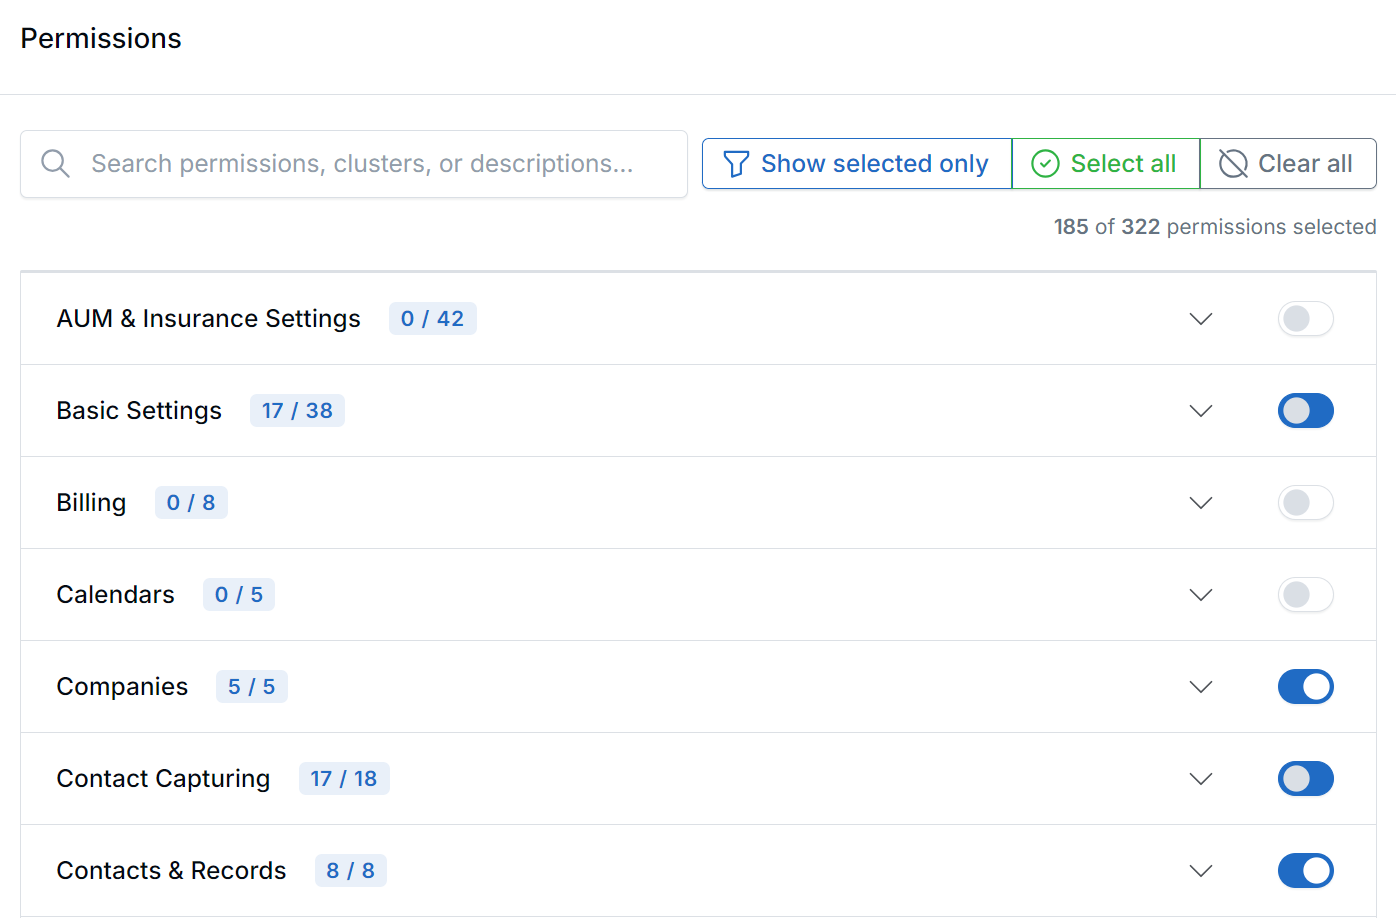
Permissions are grouped into capability groups.
| Group | Controls |
|---|---|
| Basic Settings | Business details, users, roles, teams, integrations, notifications, shared email and sending domains. |
| Contacts & Records | Merging contacts, the financials tab, exporting, SMS broadcast, record scope, and seeing private items. |
| Companies | Viewing, creating, editing, deleting, and exporting companies. |
| Contact Capturing | Form builder, external forms and websites, field mapping. |
| Database Lists | Every dropdown: stages, categories, sources, custom fields, office locations, client statuses, and more. |
| Calendars | Shared calendars and appointment settings. |
| Tasks | Viewing, creating, editing, deleting, and exporting tasks. |
| Notes | Viewing, creating, editing, deleting notes, and downloading them as PDF. |
| Documents | Viewing, adding, updating, and deleting documents. |
| Events | Events and seminars, plus attendee export. |
| Marketing | Spend and metrics, domains, landing pages, goals, marketing emails, segments. |
| Workflows & Templates | Troy AI agents, workflows, service teams, and every template type. |
| Phones & Texts | Call center, virtual numbers, SMS keywords. |
| Financial Accounts | Client accounts, account type visibility, holdings, transfers, balances, commissions, writing advisors. |
| AUM & Insurance Settings | The financial taxonomy: asset types, AUM and insurance products, custodians, fees, commission plans, wholesale providers. |
| Reports | Which report categories the user can open. Grows as report categories are added. |
| PIIs | Opening reports that show personally identifiable information (PII). Grant it only to people who need those reports. |
| Home Widgets | Which dashboard widgets appear on the Home page. |
| Security Management | Two-factor and session settings, login activities, AI chat log. |
| API Tokens | Viewing, creating, and revoking personal access tokens. |
| Billing | Subscription, trials, payment methods. |
Larger groups are divided further. Basic Settings, for example, contains sections for Business Details, Users, Roles & Permissions, Teams, Integrations, Notifications, Shared Email Account, Email Domains, Email Addresses, and Account Switching, so you can grant access to integrations without granting access to users.
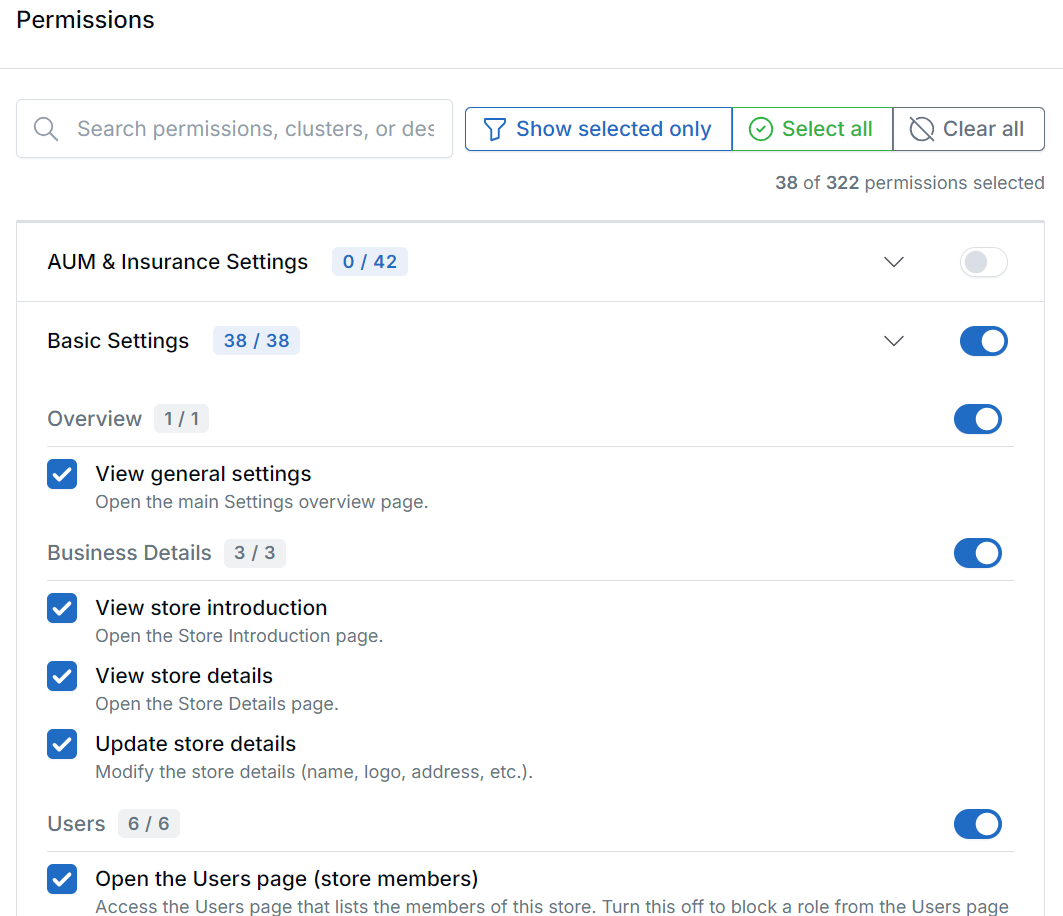
Larger groups are divided into sections.
LeadCenter hides the pages, tabs, fields, buttons, and menu items a role does not include. If someone opens a protected page directly, LeadCenter blocks it. Commission and fee amounts stay hidden unless the role includes the matching permission.
Create a Custom Role
- Go to Settings → User & teams → Roles & permissions.
- Click Create custom role.
- Enter a Role name, and a Description so colleagues know what it is for.
- Tick the permissions the role needs.
- Click Save role.
New custom roles start with nothing selected. That is deliberate: you add only what is needed rather than removing what is not.
Working through the permission list
- Search to jump straight to a permission by name or description.
- Show selected only filters to what you have already ticked. This is the quickest way to review a role.
- Select all and Clear all apply to everything currently visible.
- The counter shows how many of the total you have selected.
- Within each section, View permissions are listed first, since they are usually the ones you decide on.
Three Role Recipes
Starting points for the roles firms most commonly build.
Front desk or client service
Books appointments, answers calls, keeps contact records tidy. Grant Contacts & Records viewing, Calendars, Tasks, Notes, Events, and Phones & Texts. Leave out Billing, Basic Settings, Marketing, and Financial Accounts. Decide deliberately whether they need to see all contacts or only assigned ones.
Marketing coordinator
Runs campaigns and events, does not touch client financials. Grant Marketing, Events, Contact Capturing, Workflows & Templates, and Database Lists, plus the report categories they need. Leave out Financial Accounts and AUM & Insurance Settings entirely.
Junior advisor
Works their own book. Start from the built-in Limited role, which already lets them add and edit tasks, notes, and documents on their own contacts. Check Calendars and add it if they book their own appointments. Leave See all contacts & records off so they see only their own clients, and grant only the account types they work with.
The Two Settings That Cause Most Access Problems
These two are worth understanding before you troubleshoot anything else.
Financial Account Type Visibility
In the Financial Accounts group, an Account Type Visibility section offers three options:
- View AUM accounts
- View Insurance accounts
- View Financial Planning accounts
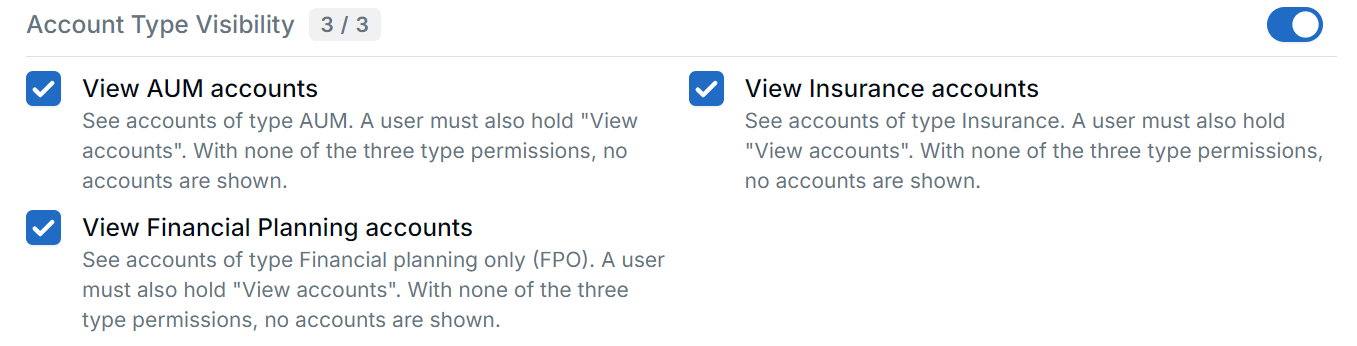
Tick at least one account type, or account lists stay empty.
View accounts on its own shows nothing. You must also tick at least one account type. With none selected, every account list stays completely empty. This is by design, not a fault. This is the single most common cause of “I have permission but I cannot see any accounts.”
See all contacts & records
In the Contacts & Records group, See all contacts & records (not just owned) decides whether a user sees everything or only their own work.
- On: the user sees all contacts and related records across the account.
- Off: the user sees only contacts where they are the owner, scheduler, writing advisor, servicing advisor, or wealth manager, directly or through a team.
This applies to Contacts, search, financial accounts, documents, calendar appointments, event attendees, financial questionnaire submissions, and contact activity. When a team is assigned, every current member of that team gets access, and access always follows the current assignment. Email, text, and call lists stay restricted to the owner or scheduler either way.
See Private Items
Users can mark notes, texts, emails, and calls private. A private item is visible only to the person who made it private, unless their role includes See private items, in the Contacts & Records group.
- The Owner role has it. Admin, Editor, and Limited don't, but you can add it to any role.
- People with it can read private notes, texts, emails, calls, and transcripts.
- They can't edit or delete someone else's private note, and they can't change whether an item is private.
Give it to the people who need to review every client conversation, such as compliance or an office manager.
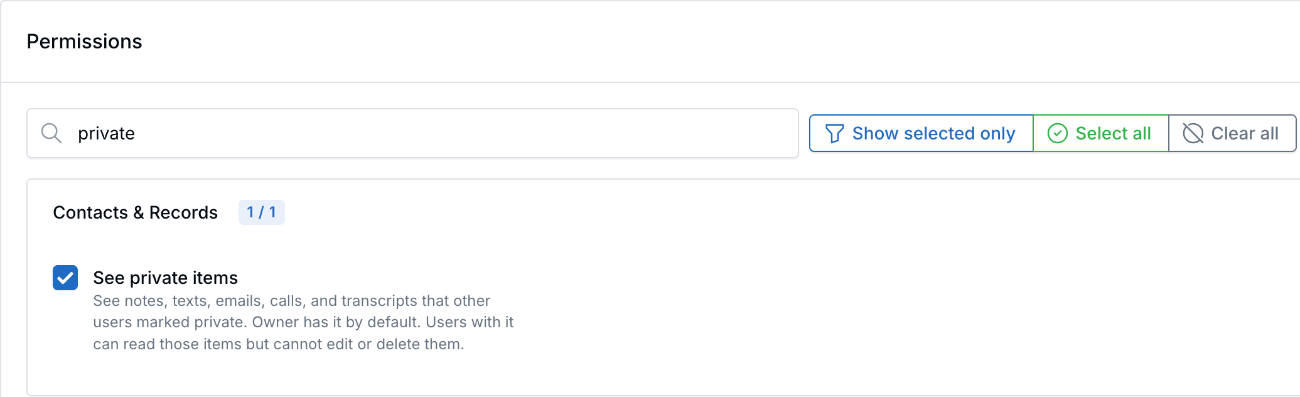
See private items sits under Contacts & Records.
Document Permissions
The Documents section of a role controls four actions:
- View documents: open the Documents page and preview or download documents.
- Add documents: upload documents from the Documents page, contacts, households, notes, tasks, and financial accounts.
- Update documents: change a document’s name, category, description, and Secure Document Portal visibility.
- Delete documents: archive or remove uploaded documents.
All four built-in roles include these by default. Which contacts’ documents a user can open still depends on See all contacts & records.
Editing and Deleting Roles
Open a role from the roles table and choose Edit (the Owner role shows View instead), adjust the permissions, and click Save changes. Changes take effect right away. Users don’t need to sign out and back in, though a page they already have open may need a refresh.
Custom roles can be deleted, but only when no users are assigned to them. Move those users to another role first.
You Can Only Give Access Your Own Role Has
When you edit a role or assign one, you can only grant permissions that your own role includes. The Owner role has every permission, so nothing changes for Owners.
- In the role editor: permissions your role doesn't have are greyed out with a lock and the note Only someone whose role has this permission can change it. Select all skips them, and saving the role keeps whatever value they already had.
- On the Users page: you can't assign a role that includes permissions you don't have. You'll see You can't give someone the [role] role because it includes permissions your own role doesn't have.
So an Admin can't give a role, or themselves, more access than the Admin role has.
Troy AI Follows the Same Permissions
Troy AI can only find, summarize, or change what the current user is allowed to access. There is no separate Troy AI permission.
- If a role cannot access a record or action, Troy declines and says so.
- Users with assigned-contact access only get results for their own contacts.
- Commission and fee details stay hidden in Troy when the user cannot see them on the account.
Best Practices
- Try the built-in roles before building your own. Owner, Admin, Editor, and Limited cover most firms.
- Build roles around jobs, not people. “Client Service” still makes sense after someone leaves; “Sarah’s role” does not.
- Grant the least access that lets someone do their work. Widening a role later is easy.
- Always check Account Type Visibility when granting account access. Without it, account lists stay empty.
Troubleshooting
A user has account permissions but sees no accounts
Their role is missing Account Type Visibility. Add at least one of AUM, Insurance, or Financial Planning.
A user can only see some contacts
See all contacts & records is off, so they see only records assigned to them. Either turn it on or assign them to the records they need.
A user can't see a note or email a colleague marked private
That's expected. Turn on See private items for their role if they need it.
A user cannot find a page they were told they have access to
Confirm the role includes the relevant View permission. Many features need it before any other permission in that group takes effect.
A permission is greyed out with a lock
Your own role doesn't include it, so you can't change it. Ask the account Owner, or someone whose role has that permission.
I changed a role but the user still sees the old version
Ask them to refresh, or to sign out and back in.
I cannot delete a custom role
Users are still assigned to it. Move them to another role first.
I cannot edit the Owner role
The Owner role is locked by design and always holds every permission. Assign a different role to that user, or contact support to transfer ownership.
Frequently Asked Questions
Can a user have more than one role?
No. Each user has exactly one.
Can there be more than one Owner?
No. To transfer ownership, contact support@leadcenter.ai.
Does editing a built-in role affect other LeadCenter accounts?
No. Your edits create a copy that belongs to your account only.
My permission list does not match this article. Why?
Every account sees the same groups. Reports appears only when your account has report categories, and its permissions are generated from those categories. Your page always shows your account’s own totals at the top.
What’s Next
Invite your team and assign their roles: Managing Users.
Need help? Email support@leadcenter.ai.

Need more help?
If you can't find the answers you're looking for, our support specialists are available to answer your questions and troubleshoot if necessary.
-
Phone Call (888) 291-7116. Our main hours are Monday to Friday 7 am-5 pm Central Time.
-
Support Send your questions and inquiries via email to support@leadcenter.ai. A support ticket will be created and one of our team members will get back to you as quickly as possible.